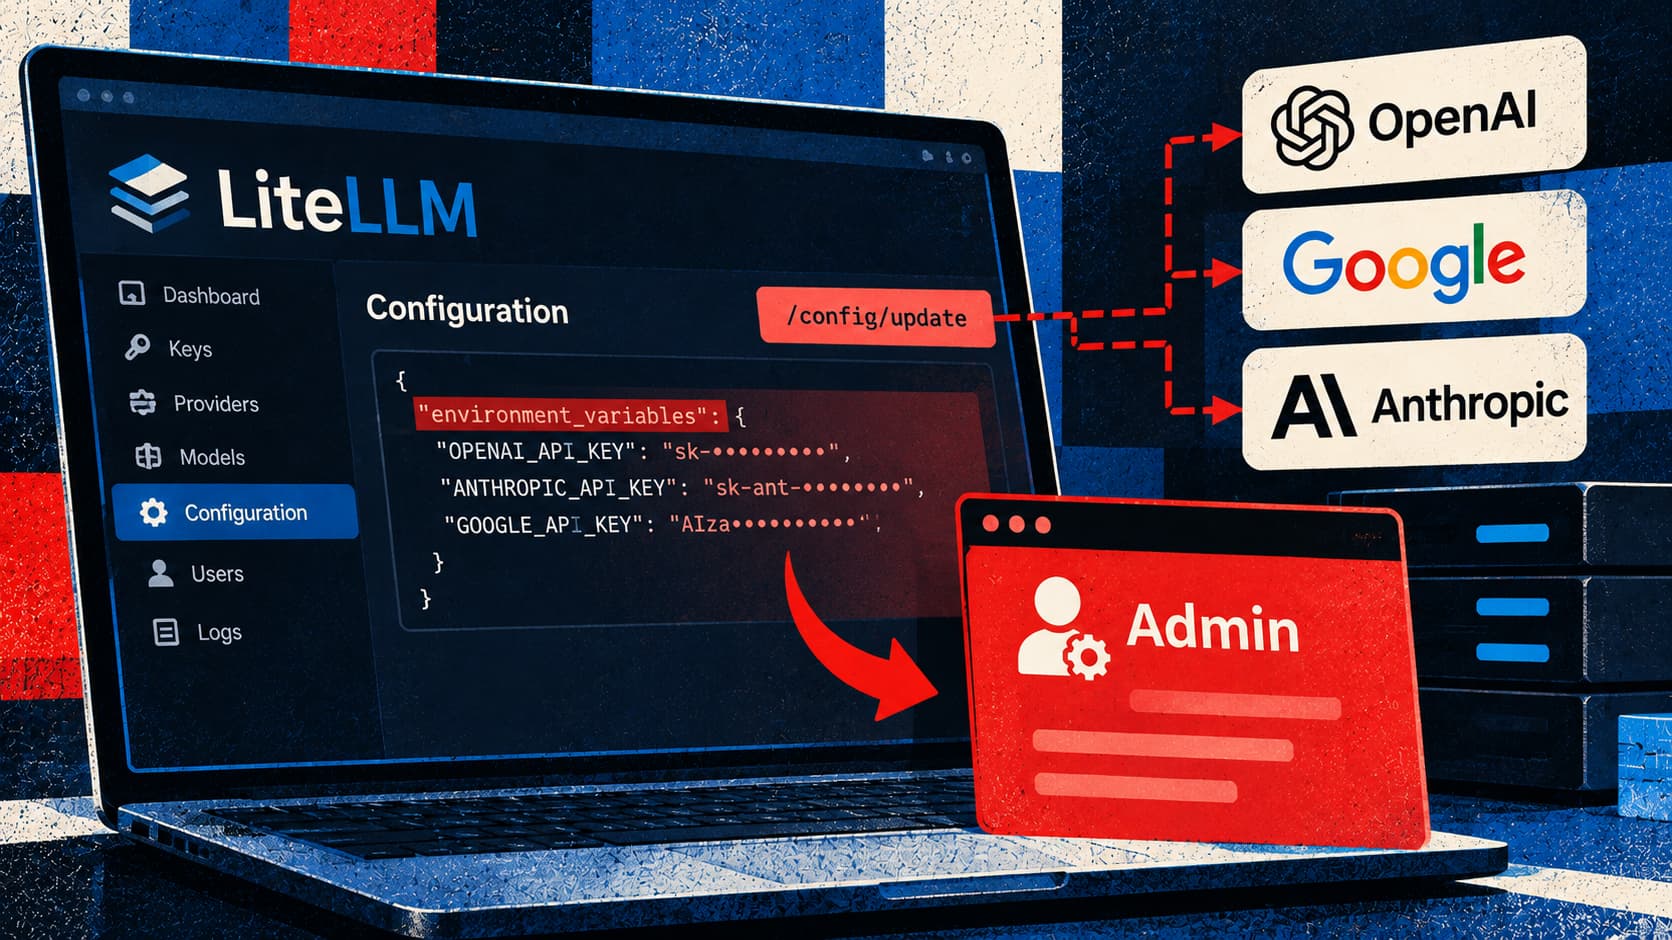
Check Point Reports LiteLLM Flaws Enabling Admin Takeover and API Key Theft
Check Point Research found two LiteLLM vulnerabilities that could let low-privilege users execute code, access sensitive files, hijack admin accounts, and steal AI provider API keys.
Adjust this page to suit you. Your choices are saved in this browser.
Cookies. Chipokia uses one cookie, and only if you allow it: a random ID so your up and down votes stay yours. No analytics, no advertising, no tracking of any kind. Cookie & Privacy Policy.