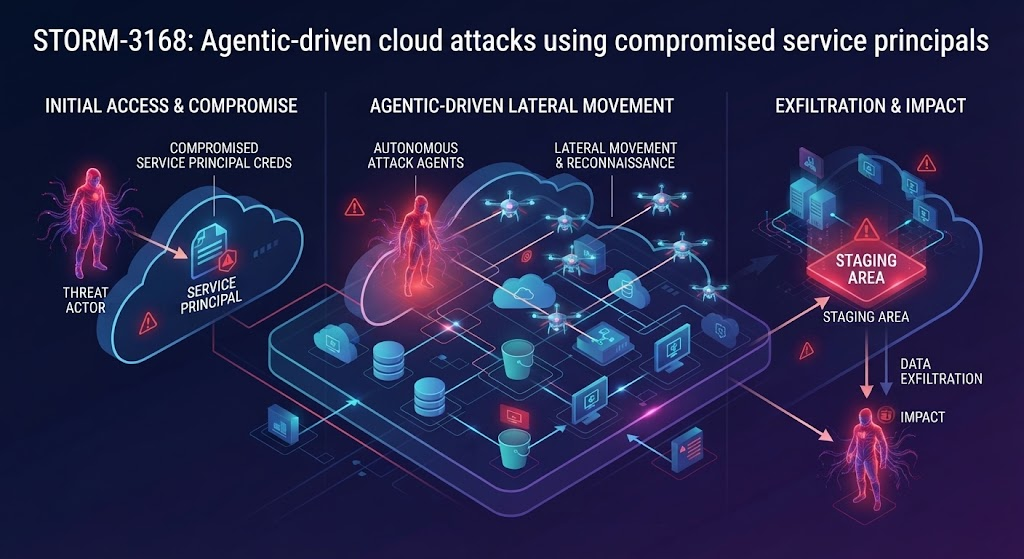
JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources
The threat actor known as JADEPUFFER has been observed orchestrating destructive actions within a Microsoft Azure environment using compromised service principals. Microsoft, which is tracking the activity under the name Storm-3168, has called it an evolution…
Adjust this page to suit you. Your choices are saved in this browser.
Cookies. Chipokia uses one cookie, and only if you allow it: a random ID so your up and down votes stay yours. No analytics, no advertising, no tracking of any kind. Cookie & Privacy Policy.